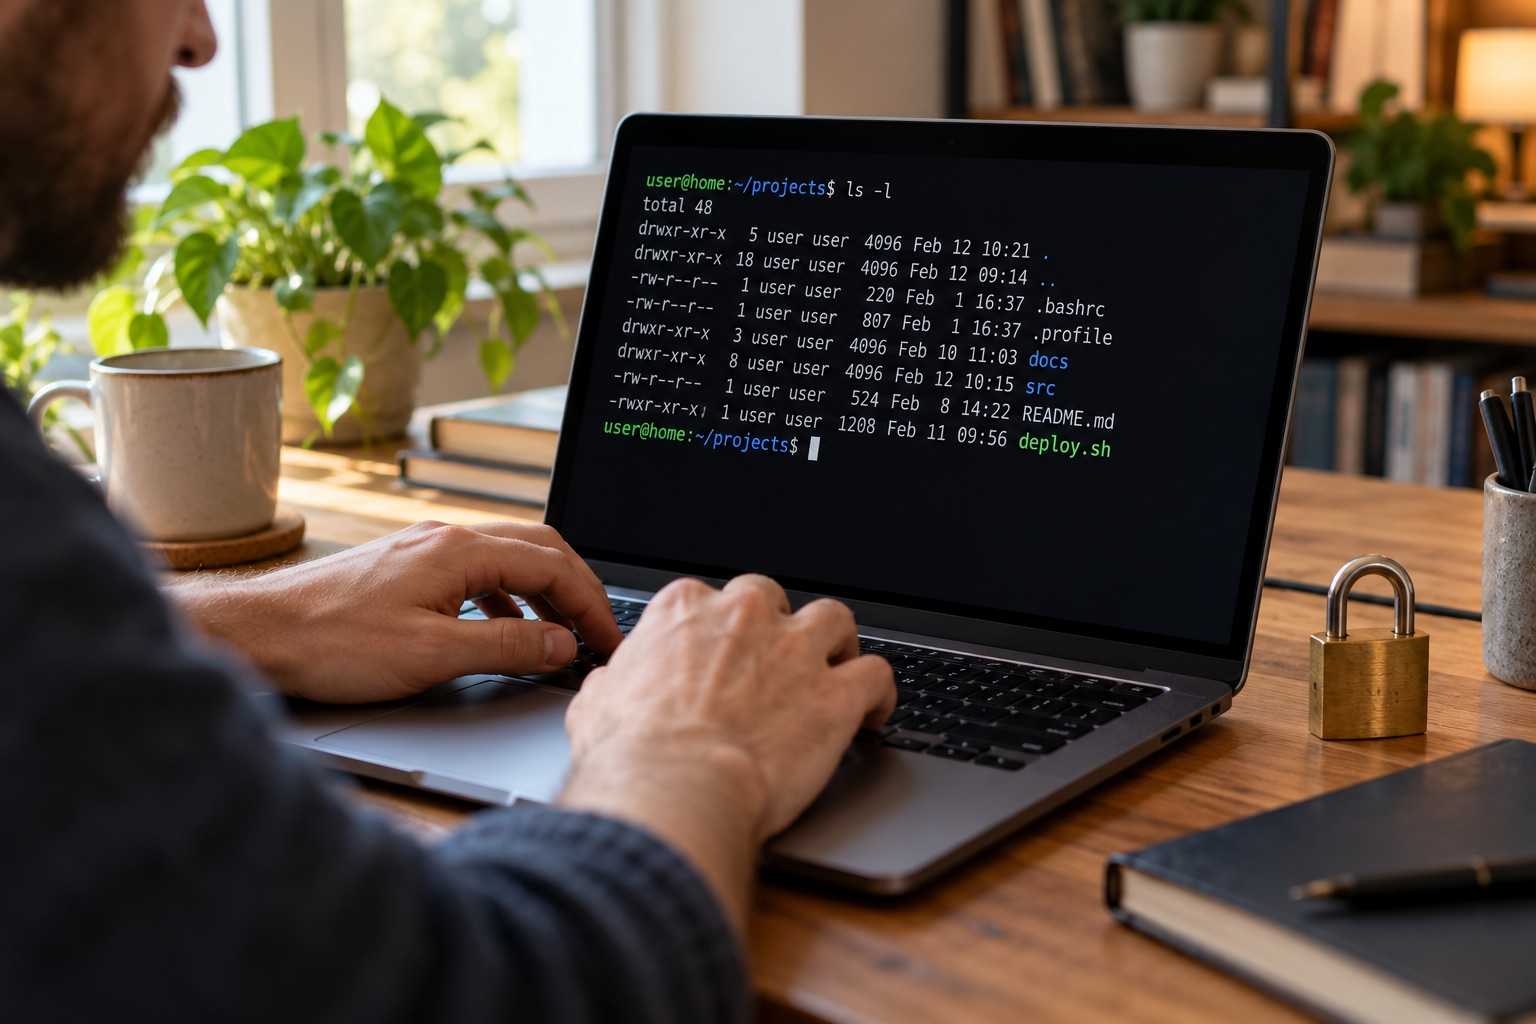
A permission error tempts operators to open access to everyone, especially when a deployment is urgent. Start with the exact machine, distribution and service at hand. A procedure that works in a tutorial may need adjustment before it belongs on a production system.
Why this deserves attention
Linux distributions offer different release schedules, package sources and support windows. Ubuntu’s security documentation is a useful example of how updates are maintained, but commands and support terms should always be checked for the distribution and version in use. A cautious change includes a backup and a way to verify the result. The correct fix may be ownership, group membership, a mount option or the service account rather than a broad file mode. The outcome must be checked after the command runs; an exit code alone does not prove the service is healthy.
A practical way forward
Inspect the file, parent directory and running process, then grant the smallest access that permits the required task. Capture the current configuration and arrange a recovery path. Make one change, inspect logs or service behaviour, and only then continue to the next step.
Picture it in a real situation
A web server that only reads uploaded images should not need write access to every directory in the project. A similar symptom on another machine may have a different cause. Keep the relevant log line and configuration change so the result can be verified later.
What to avoid
Avoid applying recursive permission changes without understanding what private keys or data live underneath. Verify the command for the installed distribution and release. A setting that fixes one server may weaken or break another if applied without context.
Takeaway
Change one thing, verify the service and retain a recovery path. That is the core of dependable maintenance.
Sources and further reading: Ubuntu security updates; Ubuntu Server documentation.