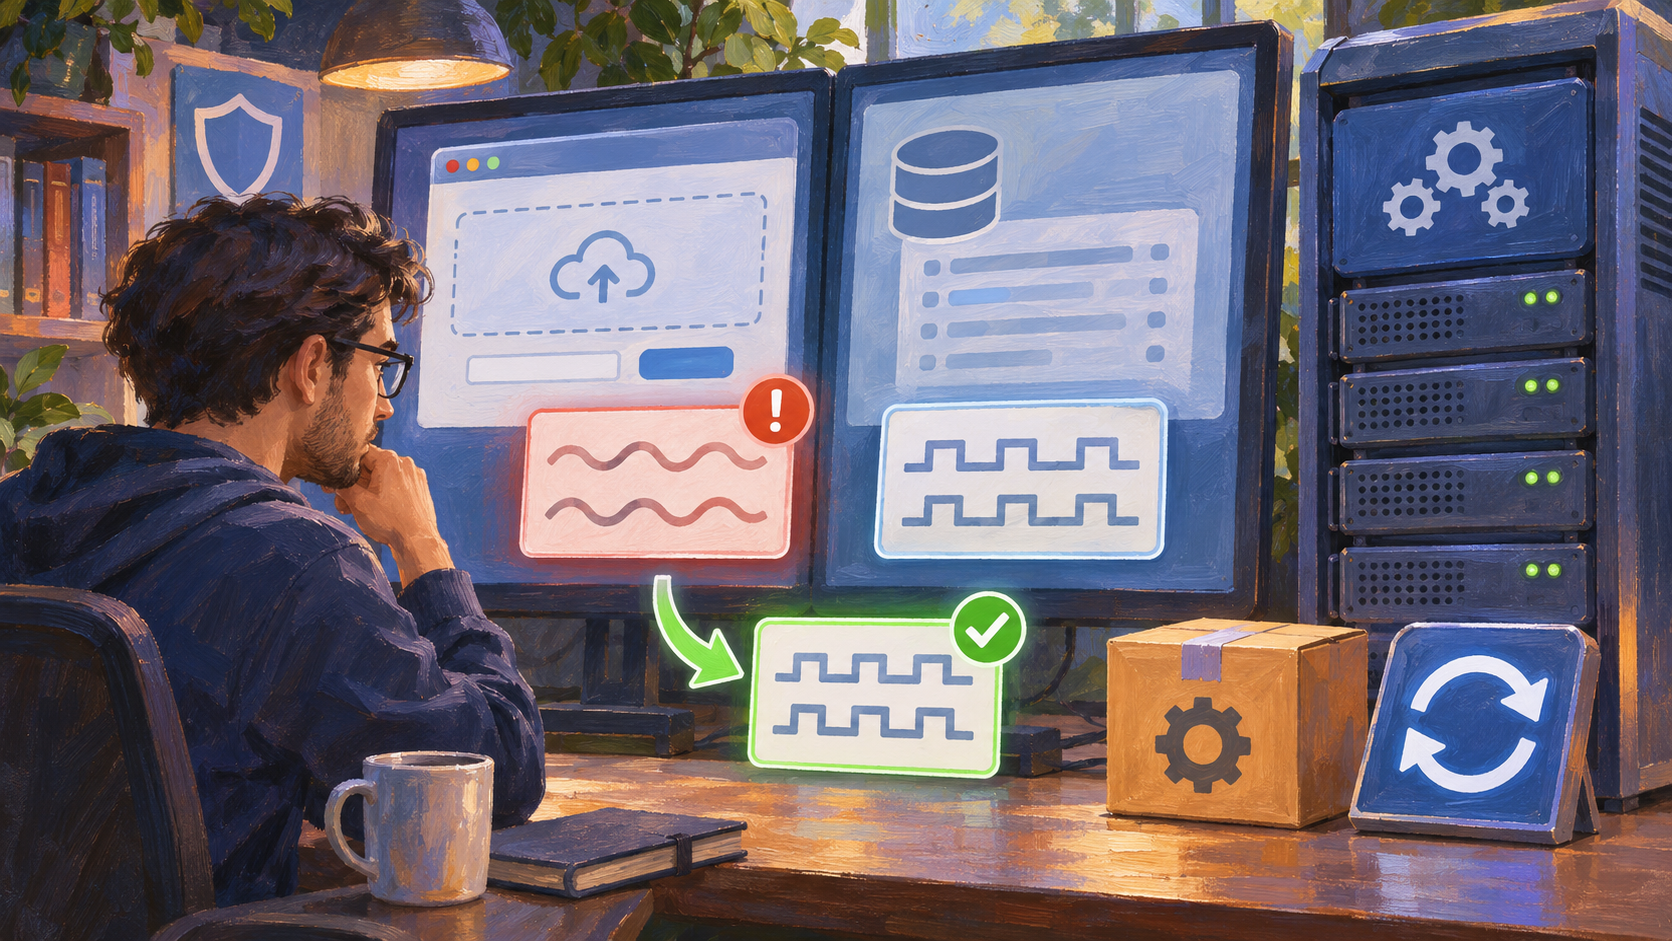
Editorial illustration: the vulnerability depends on a mismatch between the serializer used to write upload progress and the serializer used to read the shared session.
PHP released security updates on 19 November 2026 for CVE-2026-115560. The vulnerability involves PHP’s session upload-progress feature and inconsistent session serialization across applications or workers. In a qualifying setup, an attacker who can upload a multipart request may be able to create session data that a different PHP context later interprets as a serialized object. If that reader application has a suitable object gadget chain, the result may be remote code execution as the PHP worker.
The image circulating about this release is partly right: it names the four patched PHP 8.2–8.5 branches and the temporary setting session.upload_progress.enabled=0. But PHP has now shipped fixed releases. Upgrading to the supported patched release is the primary action; disabling upload progress is a mitigation for systems that cannot patch immediately. Also, php -v may report the command-line runtime rather than the PHP-FPM instance serving your site.
Summary
- CVE-2026-115560 is a session serialization mismatch involving PHP upload progress; exploitation depends on access to the relevant upload and session paths plus a suitable object gadget chain.
- PHP’s fixed releases are 8.2.36, 8.3.37, 8.4.28, and 8.5.13; verify your vendor’s package revision if it backports patches.
- The temporary mitigation is to disable upload progress in the effective server configuration, then restart PHP-FPM/workers. A late
ini_set()is not an adequate substitute. - Check the actual web runtime, shared session storage, and every application/pool that can read the same session IDs.
What the PHP advisory says
The PHP project’s security advisory describes a mismatch between the serializer used when upload progress data is written and the serializer used when that session is later read. PHP added upload progress in the 5.4 series, so unsupported older builds may also require attention even though the published fixed versions cover maintained branches.
The affected ranges in the advisory are below 8.2.36, 8.3.0 through 8.3.36, 8.4.0 through 8.4.27, and 8.5.0 through 8.5.12. PHP announced fixed releases 8.2.36, 8.3.37, 8.4.28, and 8.5.13 on 19 November. Its 8.6.0 changelog also records the fix. If your operating system or hosting provider backports the change, use its advisory and package build information to confirm the patched status rather than comparing only the upstream version string.
The CVE record is CVE-2026-115560. The advisory assigns CVSS 4.0 base score 9.2 (Critical), and lists CWE-20 (improper input validation) and CWE-502 (deserialization of untrusted data). A CVE identifier provides a common reference for the flaw; CWE describes a type of weakness; CPE is a naming scheme used to identify products and versions in vulnerability records. Those labels help organize information, but they do not prove that a particular site meets the exploit preconditions.
Why the serializer mismatch matters
PHP can store session data using different serialization formats. The advisory’s key scenario uses upload progress with one serializer, such as php_binary or php_serialize, while another PHP context reads the same session identifier with the php serializer. Because the stored bytes are interpreted differently, data controlled through the upload-progress path can be treated as serialized object data by the reader.
That reader needs a suitable object gadget chain in the application’s loaded classes for the issue to become code execution. The worker’s operating-system permissions still bound what that code can do. This is why “all PHP sites are remotely compromised” is inaccurate: a vulnerable version is a necessary concern, but the upload-progress setting, multipart upload path, shared session access, serializer mismatch, and reader-side classes all affect the scenario.
A mismatch can appear across applications, PHP-FPM pools, virtual hosts, or a CLI job if they share session storage and identifiers but use different settings. A single application’s normal requests using the same serializer do not automatically create the described mismatch. Review where session files or other session records are stored and which processes can read them.
Find the PHP that serves the website
Do not rely solely on running php -v in an SSH shell. The CLI binary may differ from PHP-FPM, a container, a hosting control panel’s selected version, or a managed runtime. Check the version reported by the web-facing PHP service using your host’s dashboard or deployment metadata, then confirm the package/build inside the relevant container or server.
For PHP-FPM, identify all pools and workers behind the site, including separate pools for admin, API, and background tasks. On a multi-node service, inspect each node or image digest. Check whether any app explicitly enables session.upload_progress.enabled, changes session.serialize_handler, or writes to shared session storage. Configuration can come from a pool file, .user.ini, php.ini, container environment, or application bootstrap; inspect the effective configuration, not just one file.
A temporary diagnostic endpoint can expose runtime details, but it should be access-restricted and removed immediately. Avoid publishing a public phpinfo() page while investigating. Prefer existing host telemetry and deployment manifests where they provide the needed runtime configuration.
Patch safely
- Map the runtime and session paths. List the PHP versions, FPM pools, applications, session storage locations, serializer settings, and upload endpoints. Mark which are publicly reachable and which share session IDs or files.
- Choose the vendor-supported fixed build. Upgrade each supported branch to 8.2.36, 8.3.37, 8.4.28, or 8.5.13 (or the vendor’s patched package). Don’t switch a production site to a different PHP branch without checking application and extension compatibility.
- Rehearse the change. Test the package in staging or a production-like environment. Exercise login, uploads, progress indicators, form submissions, and any integration that reads sessions across pools. Keep the previous deployment artifact for rollback while ensuring it is not left as the active exposed version.
- Deploy and restart all relevant workers. Replacing a package does not update already-running PHP-FPM workers. Restart or reload the service through your platform’s supported process, and roll through every node, container, or pool.
- Verify from the web path. Confirm the version/build used by the site and test real web requests. Compare running package inventory to the package manifest; a CLI version check alone is insufficient. Watch FPM logs, upload errors, authentication, and session behavior after rollout.
- Review shared-session design. If separate applications need different serializers, do not let them read the same session records. Separate storage and access boundaries, or standardize the serializer for every reader and writer. When changing the format, account for old sessions; expiring or migrating them may be necessary to avoid confusing failures.
If patching cannot happen tonight
The PHP advisory’s temporary mitigation is to set session.upload_progress.enabled=0 in the effective php.ini or pool configuration and restart PHP-FPM/workers. The change must take effect before the request is parsed. Calling ini_set() inside a script may be too late to protect the upload-progress handling that occurs earlier in request processing.
This setting can remove upload progress indicators that a site uses, so check whether the application depends on them. Apply it to every relevant web runtime, not just CLI. Record the mitigation, limit exposure of upload endpoints where feasible, and schedule the patched package as soon as practical. A WAF or upload restriction may reduce reachable traffic, but should be treated as an interim control, not as proof that the vulnerable code is fixed.
The fixed releases change the default by disabling upload progress unless explicitly enabled, and reject runtime changes to the relevant setting while upload progress is enabled. That does not automatically make different applications using shared sessions safe: administrators should still ensure that readers and writers use compatible settings and that unrelated apps do not share session records unnecessarily.
CVSS, EPSS, and what they can tell you
CVSS 4.0’s 9.2 score communicates high technical severity under the score’s assumptions. It is not a prediction that every site will be compromised, nor a complete priority ranking for your environment. Reachability, whether upload progress is enabled, shared-session access, gadget availability, worker permissions, and business impact all matter.
EPSS estimates the probability that a published vulnerability will be exploited in the wild over the next 30 days, and updates as evidence changes. No EPSS row for this CVE was returned in the 20 November 2026 check. The CVE was not present in CISA’s Known Exploited Vulnerabilities catalog at that check either. Those are date-specific data points—not a promise that exploitation is impossible or that you can delay patching indefinitely. Recheck the FIRST EPSS FAQ, CISA catalog, NVD record, and PHP advisory as they change.
Dependency scanners such as Trivy or Snyk can help find PHP base images and package versions; tools such as Dependabot can alert on application dependencies. These scanners may not know the effective FPM configuration or whether multiple apps share session storage. Pair automated findings with an inventory of the runtime and session design. For a general checklist for staging and deploying package changes, see updating Linux packages without interrupting a website and testing a backup restore before you need it.
Mistakes to avoid
- Treating the screenshot workaround as the full fix. It is a temporary mitigation; patched PHP releases are available.
- Checking only CLI PHP. The web service may use a different PHP version or container.
- Assuming every upload triggers RCE. The described outcome requires the relevant settings, shared session path, serializer mismatch, and suitable reader-side gadget chain.
- Changing serializers without planning for existing sessions. Users may be logged out or old records may be interpreted incorrectly.
- Trusting a WAF as remediation. It may reduce exposure, but it does not update PHP.
My Take
The hardest part of this advisory for many site owners may be finding the real runtime boundary. A server can report a patched CLI version while PHP-FPM continues on an older package, and two applications can quietly share session files. A short inventory of pools, upload settings, and session storage is more useful than copying a version command from a poster. Patch first, then remove the temporary mitigation only if the site has a deliberate reason to re-enable upload progress and its session design has been reviewed.
Bottom Line
Update the PHP runtime that actually serves requests to a fixed vendor build, restart every relevant worker, and verify via the web path. If an immediate update is impossible, disable upload progress before request handling and treat that as temporary. Confirm which applications share session records and whether they agree on the serializer.